

How rules are matched
Each group has Inbound Rules (traffic arriving at the server) and Outbound Rules (traffic leaving it). Rules are checked from the top down. The first match decides:ACCEPT or DROP. Put specific rules above general ones.
Create a group
1
Start the group
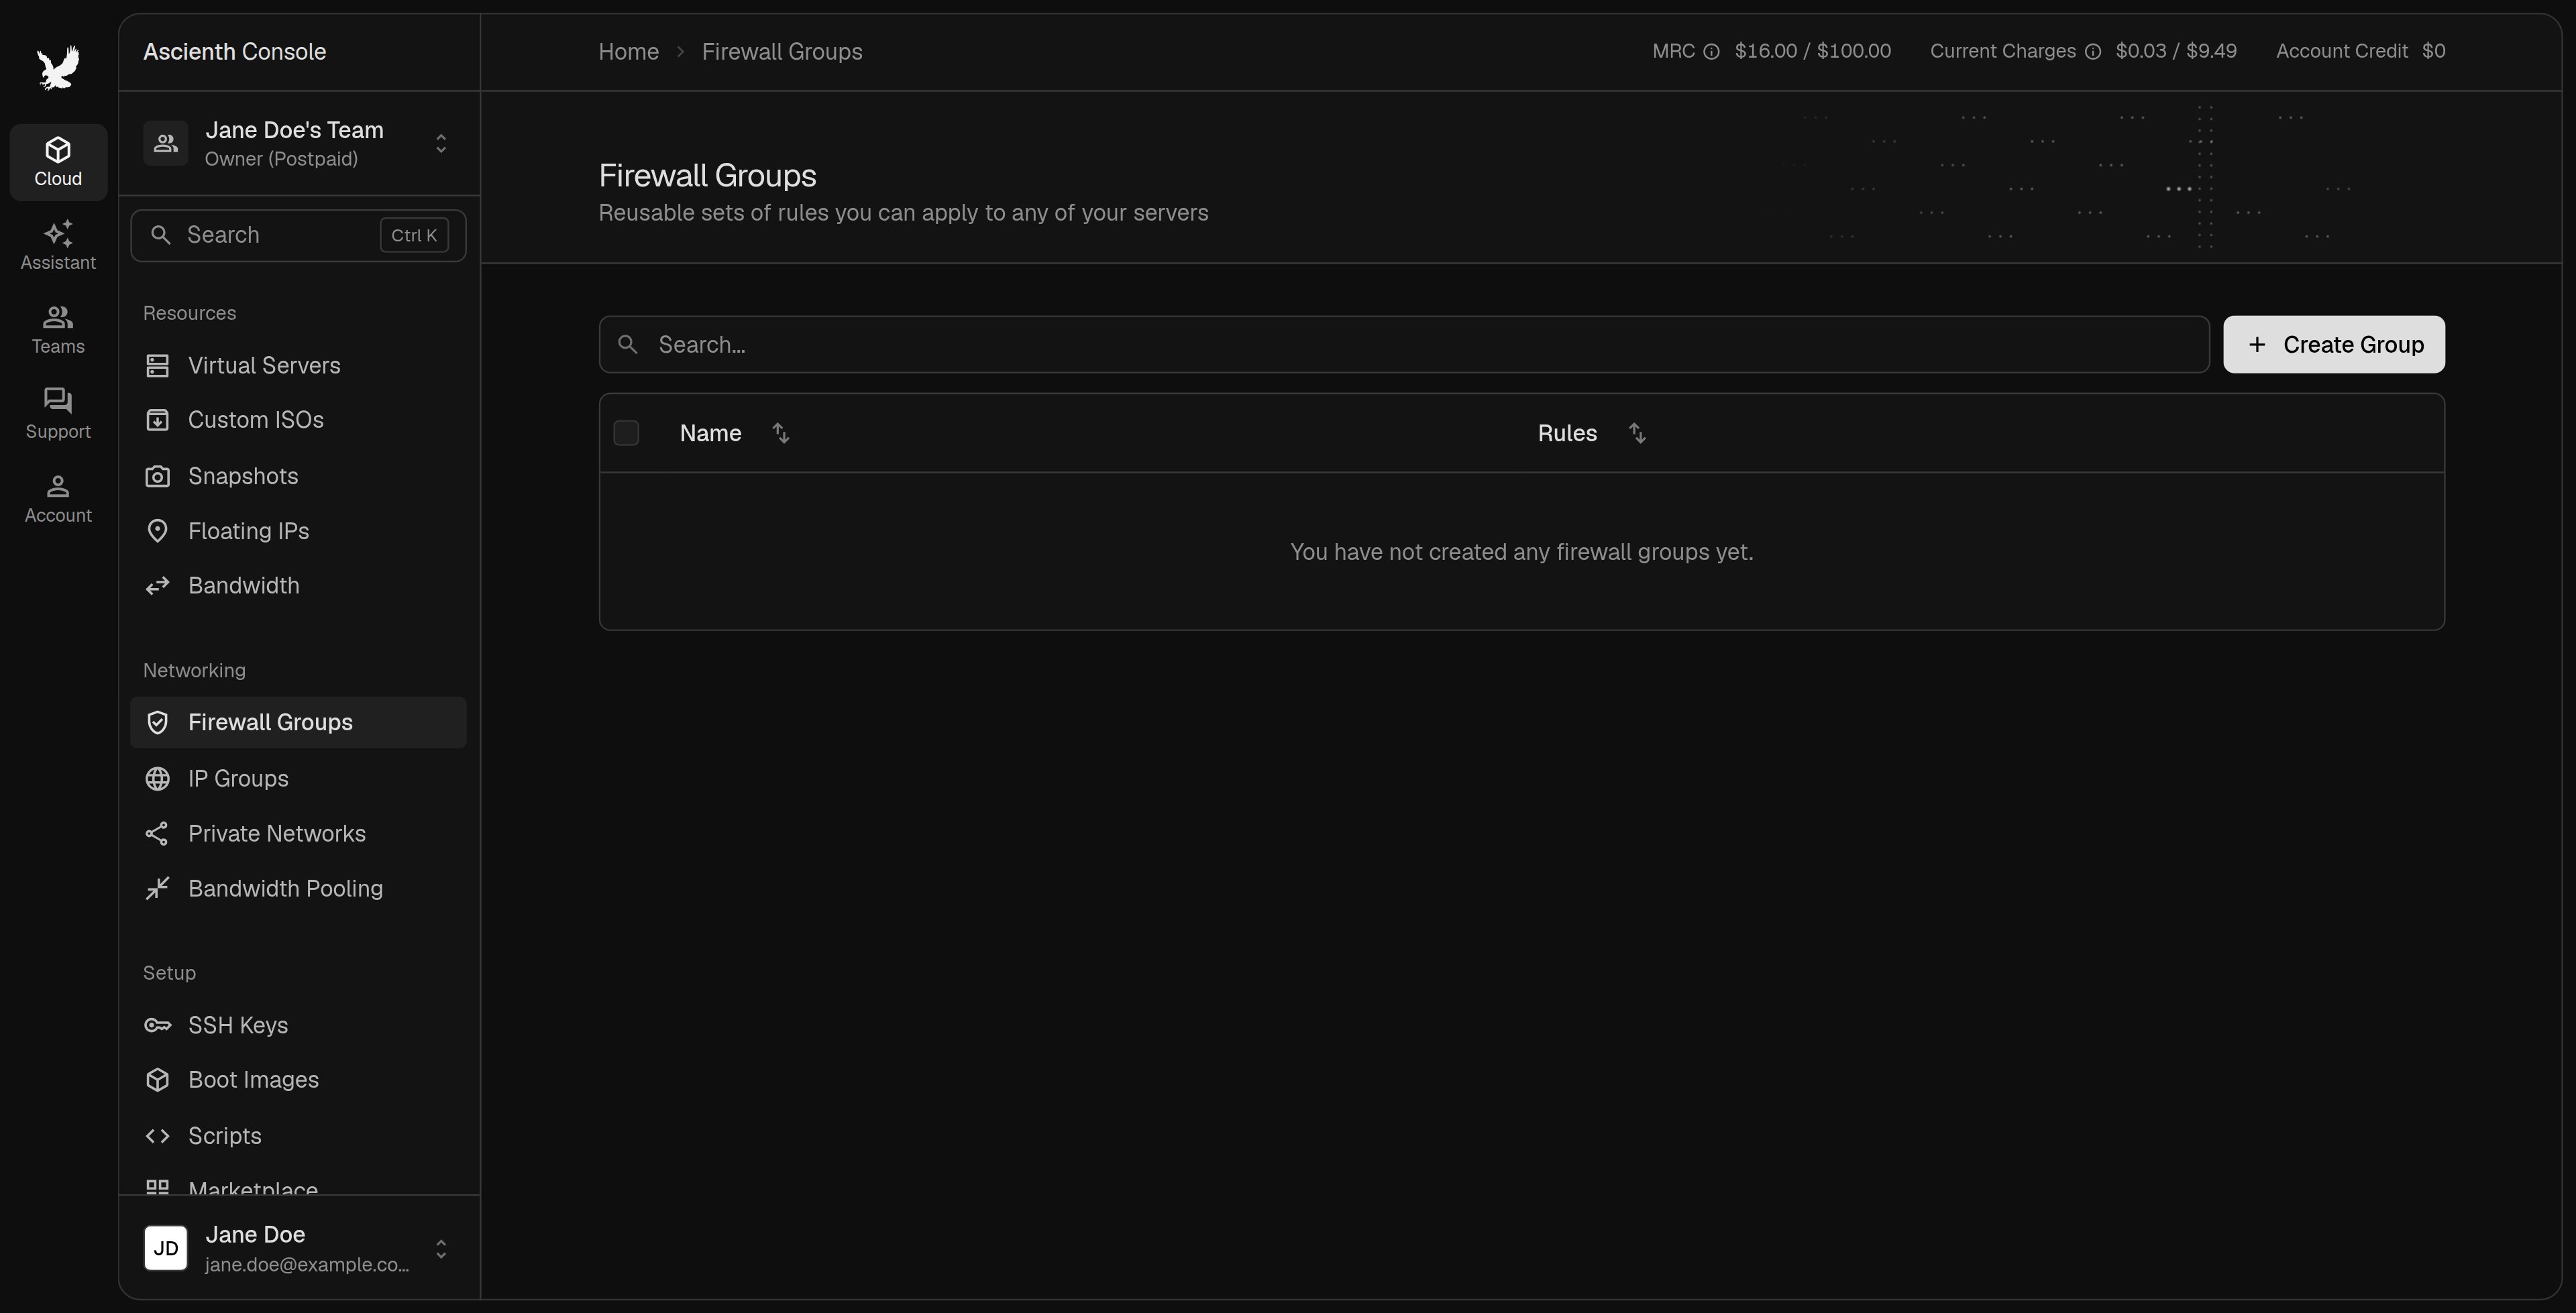
Click “Firewall Groups” in the sidebar, then
Create Group.2
Name it
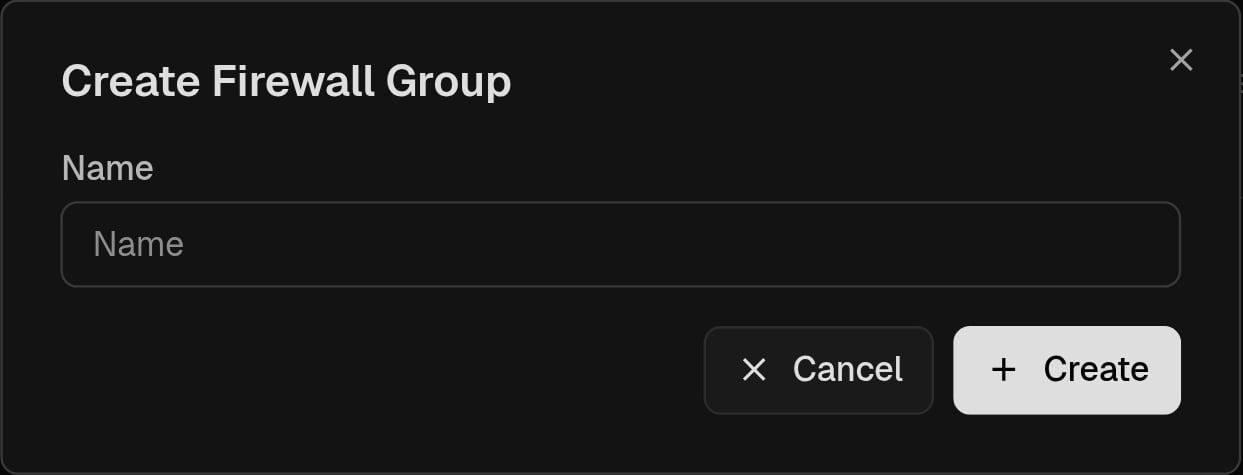
Enter a
Name and click Create. Names are unique, up to 100 characters, and may contain letters, numbers, spaces, dots, dashes and underscores.3
Open it
Click the group. It opens on the “Rules” tab.
Edit.
Add rules
1
Start a rule
On the “Rules” tab, click
Add Inbound Rule or Add Outbound Rule.2
Fill it in
Action:ACCEPTorDROP.Service (Optional): a common service such as SSH, HTTP, HTTPS, DNS, MySQL or RDP. A service sets its own protocol and ports, so those fields turn off.Protocol:TCP,UDP,ICMP,GREorNone.Port StartandPort End: the destination port. LeavePort Endblank for one port.Port Startalso takes a range like8000:8100or a comma-separated list. Ports don’t apply to ICMP, GRE orNone.Source:Any Address,Specific Address(enter it inAddress), orIP Group.
3
Save
Click
Create. The rule goes to the bottom of its list.0.0.0.0/0 and ::/0.
To reorder, open a rule’s menu and choose Move up or Move down. To change a rule, click it or choose Edit. To remove it, choose Delete and type the rule’s ID. A deleted rule is removed from every server using the group.
Apply a group to a server
1
Open the Firewall tab
Click your server, then “Firewall”.
2
Add the group
Click
Add Firewall, pick a group from Firewall and click Add. To start a new group here, choose Create New Firewall, enter a Name and click Create. It’s applied right away. Add its rules from “Firewall Groups”.3
Wait for it to apply
Attachment Status shows Syncing, then Attached. Failed means the last attempt didn’t work. Hover over it for details.Remove. The group stays on your other servers. A group’s “Servers” tab lists where it’s applied, and Remove from group works there too.
If a group’s rules can’t be applied, fix the fields and save again. If it still fails, send support the exact error and rule details. Don’t open all management ports or delete your working access rules to clear the message.
Delete a group
On “Firewall Groups”, open the group’s menu, chooseDelete and type its name.
Deleting a group removes it from every server and deletes its rules, so they stop being enforced. This can’t be undone.
IP groups
Use an IP group when several rules need the same list of addresses. Update the list once and every rule follows.1
Create the group
Click “IP Groups” in the sidebar, then
Create IP Group. Enter a Name (same naming rules as firewall groups) and click Create.2
Add addresses
Click the group, then
Add Addresses. Enter one address or CIDR range per line, such as 203.0.113.7 or 203.0.113.0/24. Add a Note if you like, then click Add. Duplicates are skipped. A span like 1.2.3.4-1.2.3.9 isn’t accepted, so write it as CIDR ranges.3
Use it in a rule
Set the rule’s
Source to IP Group and pick the group.Good to know
Does the firewall filter my private network?
Does the firewall filter my private network?
No. Traffic on a private network isn’t filtered by the console firewall. Use a firewall inside your server.
Can I open port 25 with a rule?
Can I open port 25 with a rule?
No. Outgoing port 25 is blocked separately. See Port 25 Unblocking.
Can I use one group on servers in different locations?
Can I use one group on servers in different locations?
Yes. Groups aren’t tied to a location. Apply one to any server in the team.