

View servers. Changing addresses needs Change networking. Buying or cancelling an address needs Make purchases. The team owner can do all of it.
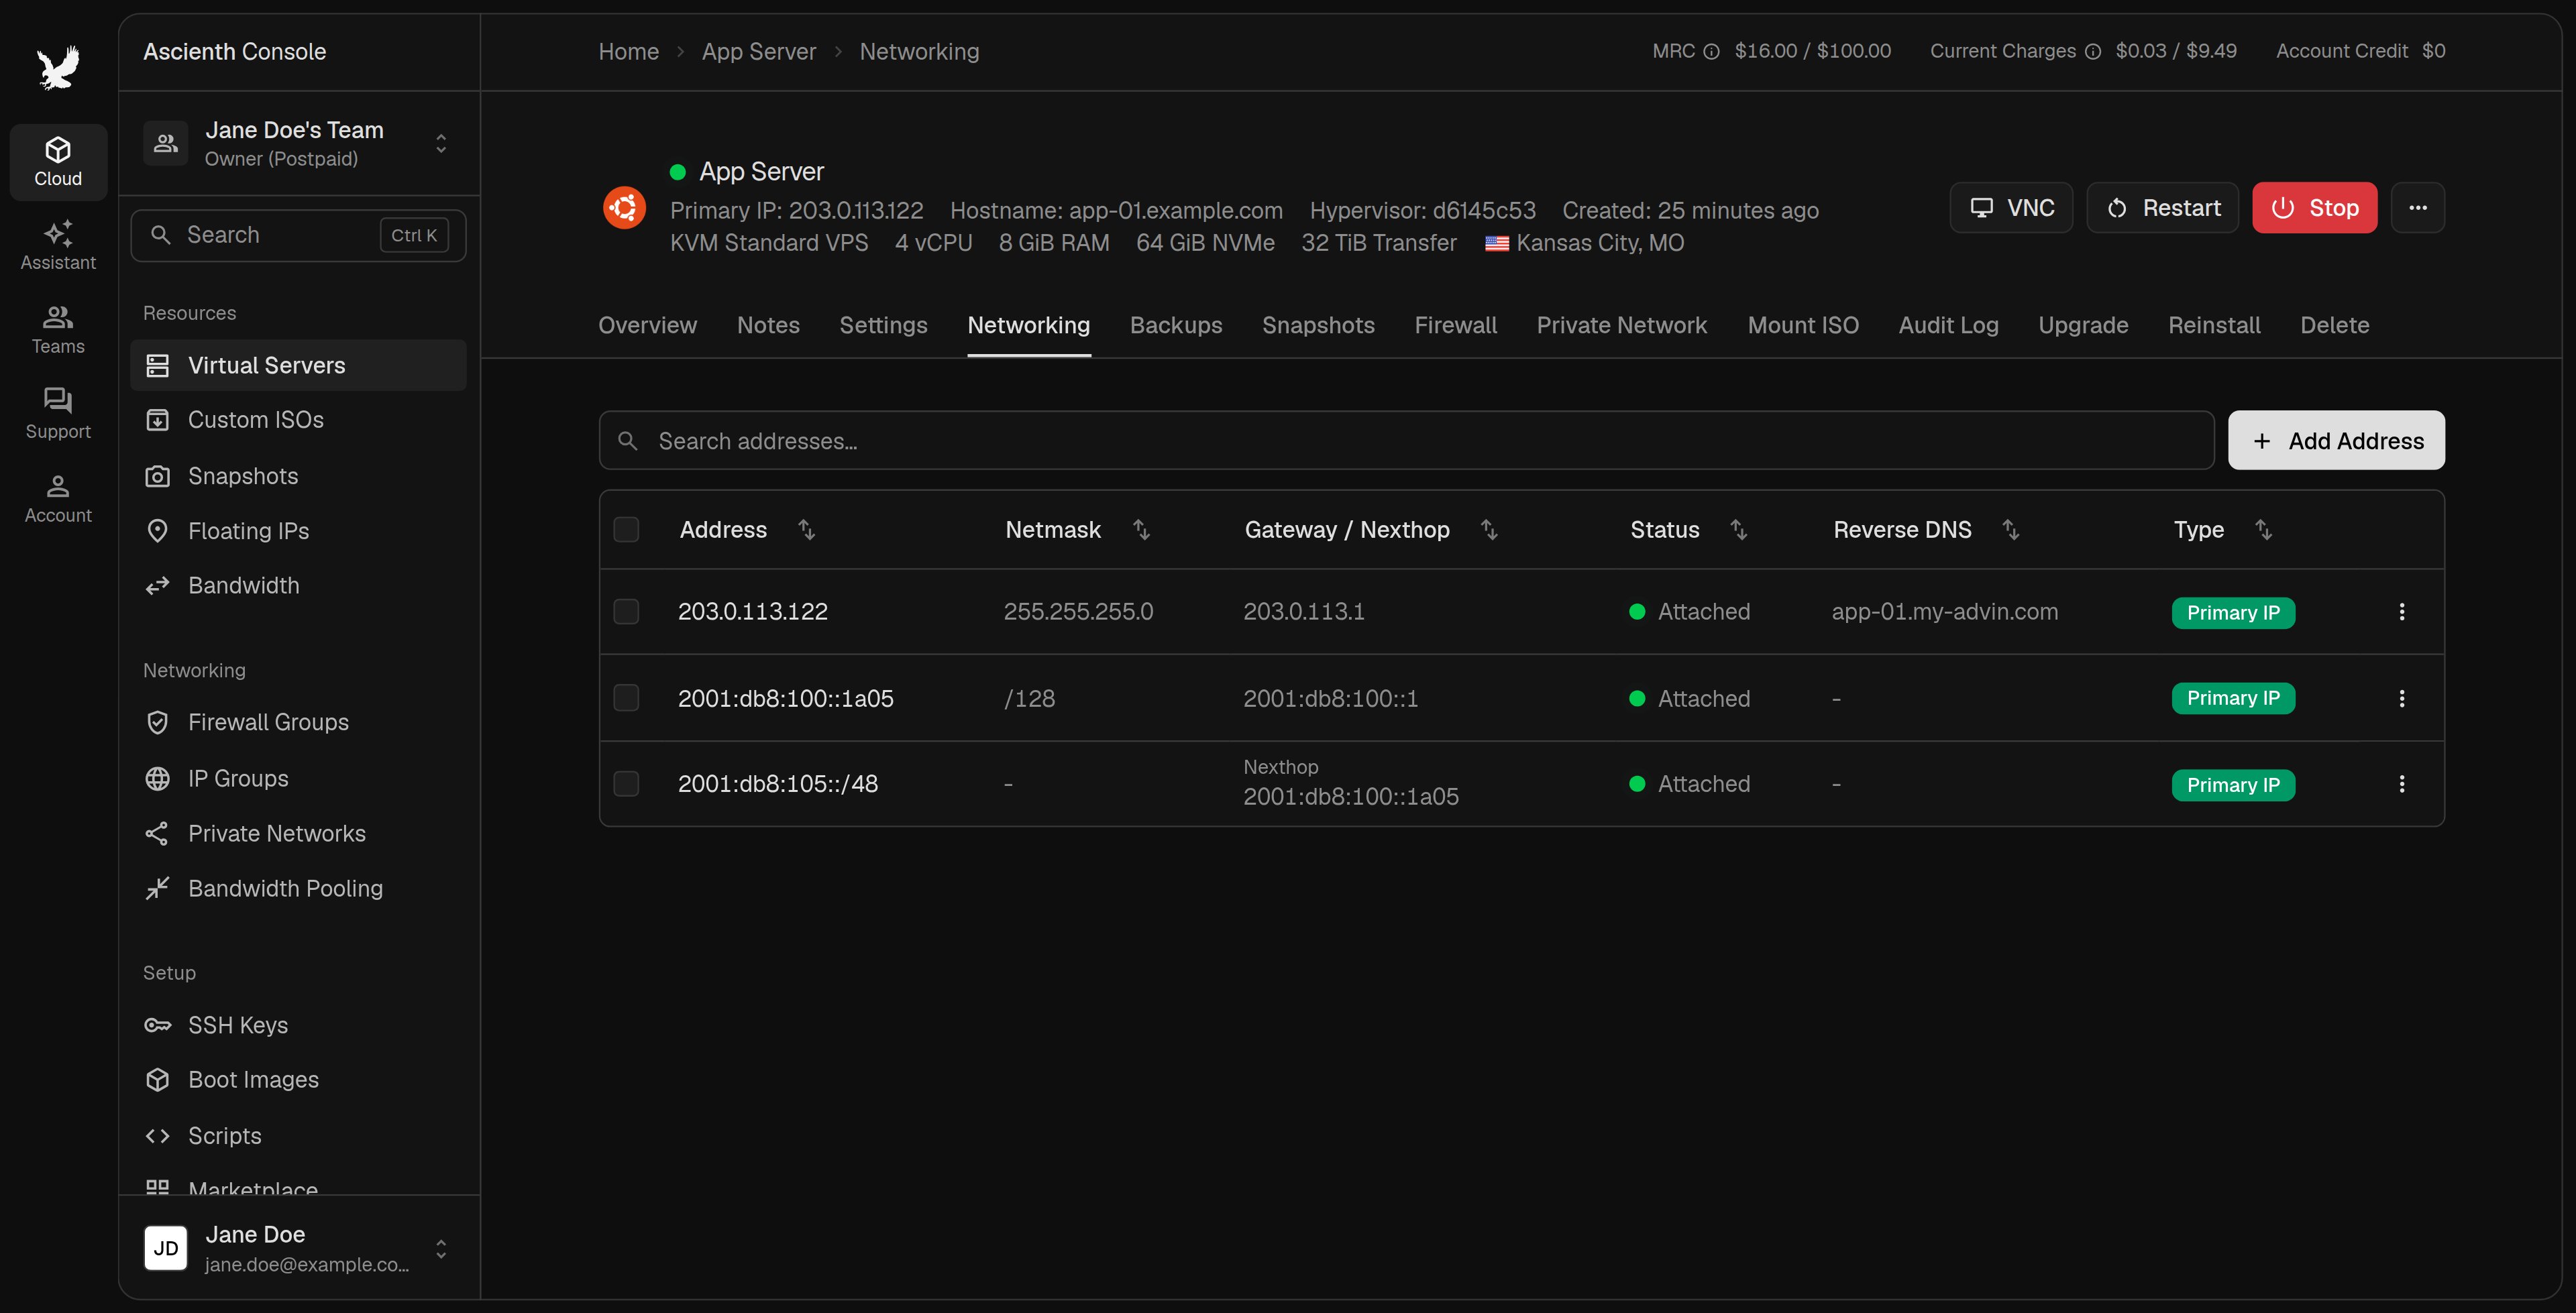
Read the address table
Each row’s menu shows only the actions your role allows. For reverse DNS, see Reverse DNS.
Add an address
1
Open the dialog
Click
Add Address above the table.2
Choose the address
Pick one of your floating IPs from
Address. Only addresses that aren’t attached elsewhere and can reach this server are listed.To buy a new one, choose Create a new floating IP and pick IPv4 or IPv6 under Address type. The Price field shows the cost. Prepaid teams pay from account credit. Postpaid teams are billed hourly on the monthly invoice.3
Confirm
Click
Attach address, or Buy and attach for a new one. Status shows Attaching, then Attached.Detach or cancel a floating IP
Detachtakes the address off this server. You keep it and keep paying for it, and you can attach it to another server later. Anything using it here stops responding.Cancel addressends the rental. See cancelling an address.
Detach in the bar that appears. Only floating IPs can be detached. To get rid of a primary address, make another IPv4 primary first.
Change the primary IP
Open an attached floating IPv4’s menu and chooseSet as Primary. The two addresses swap roles, and the old primary becomes the floating IP you rent. Only IPv4 can be primary. The full procedure is in Change Your IPv4 Address.
If the option is missing, you need Change networking and another attached IPv4 that is active, paid and not scheduled for cancellation. Wait for any running server operation to finish.
IPv6 allocation
Use the address, prefix and gateway shown on your server’s “Networking” tab. Layouts differ between locations and servers. A typical allocation is one on-link address plus a routed subnet. Some locations use an on-link subnet instead.
A routed range isn’t configured inside your operating system for you. Pick addresses from the range and add them yourself. You don’t need a floating IP for each one. Keep the working on-link address and default route, and save the configuration so it survives a reboot.
To check what’s configured, run these on Linux:
ipconfig /all and route print -6. Keep VNC open while you edit network settings so you can recover if remote access drops.
Containers and VPNs behind a routed subnet need forwarding, routing and firewall rules inside the server. On Ubuntu with Netplan, see the Netplan tutorial. Don’t paste a template written for a different interface or server over a working config.
If IPv4 works but IPv6 doesn’t:
- Check that your own network supports IPv6.
- Check the address, prefix, gateway, the firewall inside your server, and that the application listens on IPv6.
- If only a hostname fails, check its
AAAArecord.
DDoS Manager
The “DDoS Protection” tab lets you add filtering rules for protected IPv4 addresses. It exists only for servers in Nuremberg, DE. Our other locations don’t offer DDoS filtering. See DDoS Protection for how filtering works and which presets exist. Pick an address fromIP Address at the top. The table lists its rules by Protocol, Preset, Min Port, Max Port and Created. Viewing needs View networking, creating rules and changing settings needs Change networking, and deleting rules needs Delete networking resources.
Create a rule
1
Open the dialog
Click
Create Rule.2
Pick the protocol and preset
Choose the
Protocol: TCP, UDP, ICMP or GRE. Preset then lists only the presets for that protocol.3
Enter the ports
For TCP and UDP, enter the port in
Min Port. For a range, also fill in Max Port (optional). Without it, the rule covers one port. Ports run from 1 to 65535.4
Create the rule
Click
Create.Delete and type the rule’s ID.
Address settings
The “IP Configuration” card holds two settings for the selected address. Change them and clickSave Changes.